LIVE Checkout Page — https://prayersong.com/create/checkout
- Extracted: 2026-09-14, live walkthrough (viewed only — NO payment details entered, NO purchase submitted, per task safety rules)
- Full URL observed:
https://prayersong.com/create/checkout?session_id=pi_3UFfVtIDReRVUvxp0m8ez1f9&survey_id=279aa19e-e141-4745-8893-36589b81b7e4 - Screenshot: screenshots/live-04-checkout-page.png
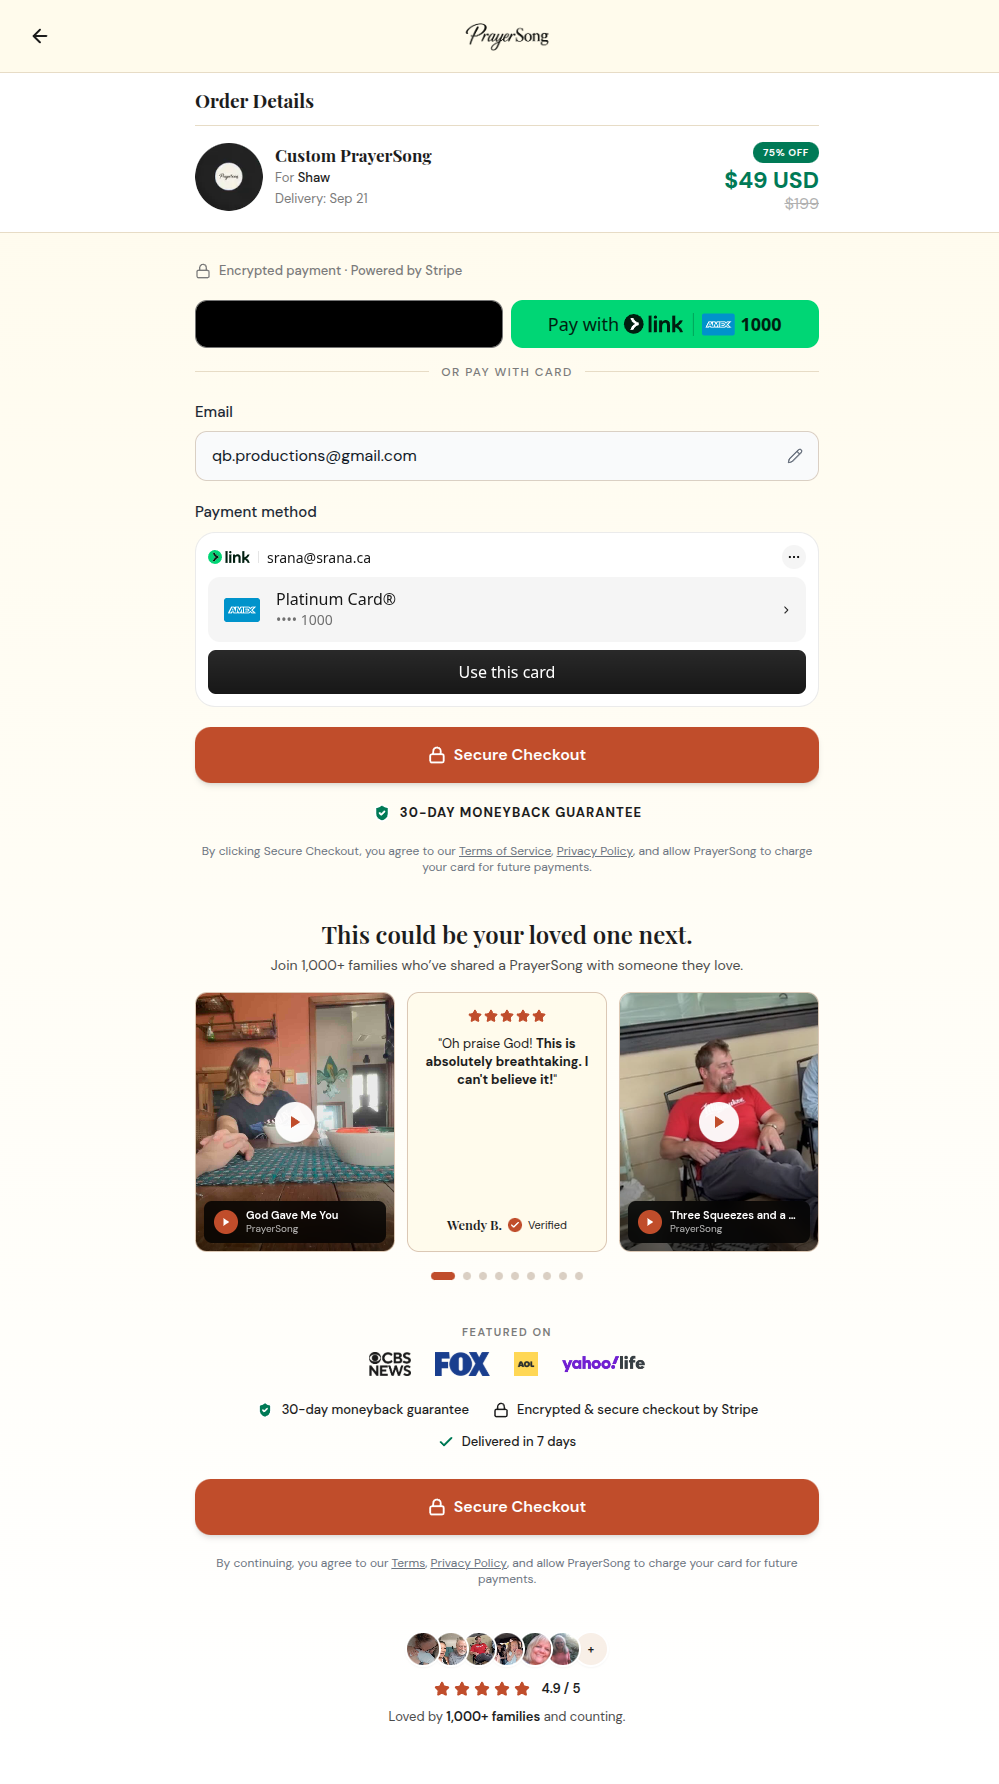 (full page, empty/unfilled payment form)
⚠️ Key technical finding: checkout implementation has changed since the community's capture
The Dec 2025 community capture (Lesson 7) showed a redirect to a hosted Stripe Checkout page (checkout.stripe.com-style full-page takeover with Google Pay/Link/Card tabs). The live site today uses an embedded Stripe Elements checkout on their own domain (prayersong.com/create/checkout), with:
- A
session_idquery param that is a Stripe PaymentIntent ID (pi_3UFfVtIDReRVUvxp0m8ez1f9) — confirming a PaymentIntent is created before the buyer enters card details (standard Stripe Elements/Payment Element pattern). - A
survey_idquery param linking the checkout session back to the survey response (279aa19e-e141-4745-8893-36589b81b7e4). - Two embedded iframes: a "Secure express checkout frame" (Apple Pay/Google Pay/Link one-click buttons) and a "Secure payment input frame" (card fields), both Stripe-hosted iframes embedded in the PrayerSong page rather than a full off-site redirect.
This is a meaningfully different (and more modern) checkout architecture than what the community documented — worth flagging since it changes the buildout approach if replicating this funnel (Stripe Elements/Payment Element integration vs. simple Stripe Checkout Session redirect).
Full verbatim page copy
- Logo: PrayerSong (transparent logo)
- Heading: "Order Details"
- Line item: "Custom PrayerSong" — "For Shaw" — "Delivery: Sep 21" — badge "75% OFF" — $49 USD (was $199)
- Trust line: "Encrypted payment · Powered by Stripe"
- "OR PAY WITH CARD" divider (below the express-checkout iframe)
- Field: "Email" (pre-filled, read-only, showing the email entered on the prior page) + "Change email" button
- "Payment method" (embedded card-input iframe, empty/unfilled)
- Primary CTA: "Secure Checkout" (×2 — one immediately below the payment fields, one repeated further down the page after the testimonial section)
- Trust line: "30-DAY MONEYBACK GUARANTEE"
- Legal: "By clicking Secure Checkout, you agree to our Terms of Service, Privacy Policy, and allow PrayerSong to charge your card for future payments." (repeated near the bottom CTA too, worded "By continuing, you agree to our Terms, Privacy Policy, and allow PrayerSong to charge your card for future payments.")
Social proof section — "This could be your loved one next."
Join 1,000+ families who've shared a PrayerSong with someone they love.
- 9-testimonial carousel (expanded from the 3 shown on the sales page) with playable "testimonial video" buttons: God Gave Me You, Three Squeezes and a Miracle, My Heart is Yours, Mommy's Love, God's Promise, Chosen Hearts, I Still Believe, plus 3 more (carousel dots go up to 9, only a subset of titles were visible in the accessibility tree without scrolling the carousel).
- Visible quotes: Wendy B. ("Oh praise God! This is absolutely breathtaking. I can't believe it!"), Markeeta B. ("Very very wonderful song. I absolutely loved it and so did Dave!..."), Pamela S. ("Absolutely beautiful, you captured such special moments… we both were crying...").
- Press badges: "FEATURED ON" — CBS, Fox, AOL, Yahoo Life (each an expandable detail button).
- Trust bar: "30-day moneyback guarantee" / "Encrypted & secure checkout by Stripe" / "Delivered in 7 days"
- Rating: "4.9 / 5" — "Loved by 1,000+ families and counting." (new star-rating number not seen anywhere in the community's Dec 2025 capture)
Outbound links
None extractable as plain hrefs — Terms/Privacy are in-page modal-trigger buttons, not separate URLs, on this embedded checkout page.
Key numbers cited
- Price at checkout: $49 USD (was $199, 75% off) — consistent with landing/sales page.
- New rating figure: 4.9 / 5 stars.
- Testimonial carousel expanded to 9 items (vs. 3 on the Dec 2025 checkout/sales pages).
- Stripe integration confirmed as PaymentIntent + Payment Element (embedded), not hosted Stripe Checkout redirect.
What was NOT done (safety compliance)
Per task rules, no card number, expiry, CVC, or billing details were entered into the payment iframe, and the "Secure Checkout" button was never clicked. The page was reached, documented, and screenshotted in its empty/default state only. No upsell, post-purchase, or thank-you pages were reachable beyond this point since they require a completed real payment — those are documented instead via the community's actual test-purchase screenshots and downloaded receipt/email PDFs (see ../08-checkout-page.md through ../12-followup-email-reaction-video.md and ../14-post-purchase-email-sequence.md).